Ethereum Post-Quantum Security Roadmap
Ethereum Post-Quantum Roadmap and Account Migration Strategies in 2026
RSA-896 was factored on September 19, 2026 after Claude helped adapt CADO-NFS for graphics processors and coordinate up to 2,048 processors. The computation lasted about 10 days and consumed roughly 30 graphics-processor years, according to Stephen Weis’s primary account. The widely repeated “16 days” refers to the interval between the RSA-260 and RSA-896 records, not the runtime of the second factorization, as the Ars Technica coverage explains.
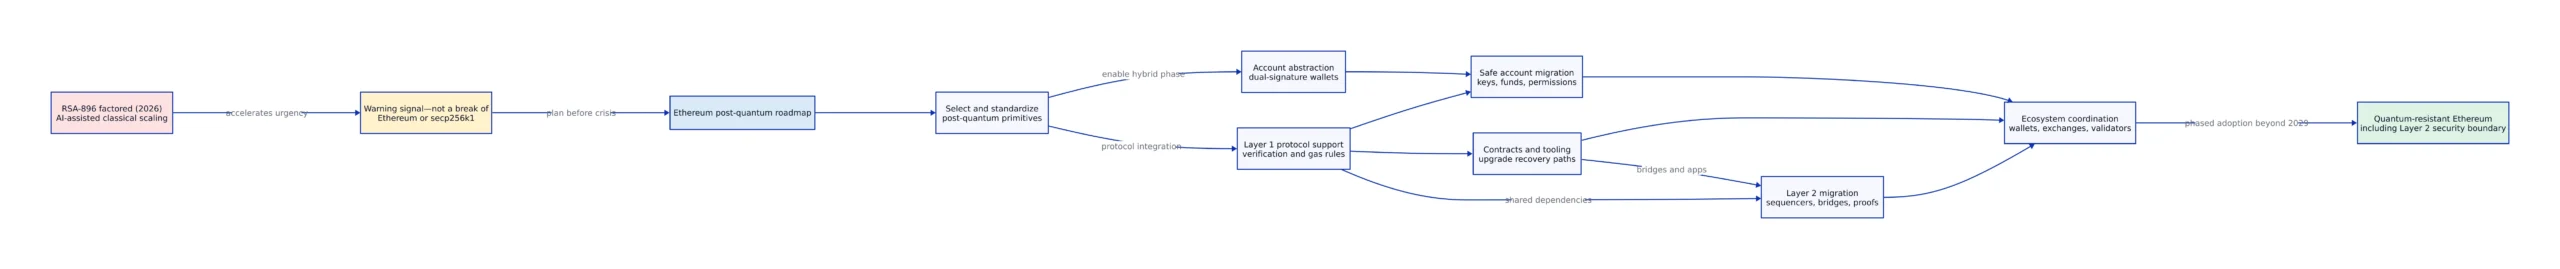

The result leaves Ethereum, secp256k1, and RSA-2048 unbroken, while showing that classical factoring assisted by artificial intelligence can reduce the engineering effort needed to apply established cryptanalysis on large graphics-processor fleets. Ethereum’s response involves managing migration and coordination: introduce replacement primitives early, move accounts safely, and include Layer 2 systems instead of treating the base chain as the entire security boundary.
Key Takeaways:
- RSA-896 was a classical factoring record, not a classical attack on Ethereum’s elliptic-curve account keys.
- The Ethereum Foundation’s post-quantum team says Layer 1 upgrades could reach the planned state by 2029, while execution-layer adoption will take additional years.
- Account abstraction can let a smart account change its authorization logic, but safe migration also requires disabling old elliptic-curve authorization paths.
- Rollups must update operational keys, bridge controls, user accounts, and pairing-based proof systems. A base-layer signature change does not secure those dependencies automatically.
- Developers should inventory exposed keys, test recovery and rotation, avoid unnecessary address reuse, and monitor Hegota discussions without calling Glamsterdam a post-quantum upgrade.
The Impact of RSA-896 Factoring on Ethereum’s Security Assumptions
Ethereum externally owned accounts use the Elliptic Curve Digital Signature Algorithm over secp256k1, not RSA. The general number field sieve factors an RSA modulus; it does not solve the elliptic-curve discrete logarithm problem behind an Ethereum account. Weis also states that the RSA-896 work did not meaningfully improve the algorithm and does not affect deployed RSA-2048 keys in his technical disclosure.
The record still changes one planning assumption. Specialist implementation work and large-job coordination can become cheaper before the underlying mathematics changes. Ethereum cannot assume that migration will begin only after a new algorithm appears. Wallet support, contract compatibility, custody approval, and user action each require more lead time than a software port.
- Audit distinction: keep RSA key retirement and Ethereum account migration as separate workstreams.
- Incident classification: no CVE has been assigned because RSA-896 is a factoring benchmark, not a vulnerability in a named product.
- Monitoring: track unexpected long-running graphics-processor jobs and unapproved cryptanalytic software in shared computing environments.
Classical Factoring and Blockchain Key Security
RSA-260 was factored 16 days before RSA-896. For RSA-896, Claude assisted with porting CADO-NFS and orchestrating idle computing capacity, while the general number field sieve remained the mathematical method. This is better described as classical factoring assisted by artificial intelligence than an autonomous discovery of a new attack.
Public ledgers keep signatures and public-key evidence, so exposed keys remain easy to identify later. An Ethereum account that has sent a transaction has exposed the information needed to recover its public key, while an account that has only received funds retains the limited protection of an address derived from a public key, as the Ethereum quantum-resistance page explains. A sufficiently capable quantum computer could then target that exposed key, but the RSA record does not provide a classical method to do so.
Ethereum’s Post-Quantum Roadmap and Timeline
The Ethereum Foundation’s post-quantum team sets 2029 as a target for Layer 1 protocol upgrades, not a date when every wallet, contract, exchange, and rollup becomes safe. Its published roadmap says full execution-layer migration will take additional years and that the milestones remain subject to research, implementation, and Ethereum’s open governance process. Secondary reporting describes five planned hard forks through December 2029, but the official roadmap presents directional milestones rather than guaranteed release commitments.
| Security surface | Existing dependency | Planned transition direction | Source |
|---|---|---|---|
| User accounts | ECDSA over secp256k1 | Account abstraction and post-quantum signature verification | Ethereum.org |
| Validator consensus | BLS signatures | Hash-based signatures with proof-based aggregation | Post-Quantum Ethereum |
| Data availability | KZG polynomial commitments | Post-quantum blob commitments and sampling | Post-Quantum Ethereum |
| Layer 2 systems | Operational keys, bridges, user accounts, and proof systems | Separate upgrades at each trust point | Post-Quantum Ethereum |
Glamsterdam should not be described as a post-quantum standard or a quantum-security release. The Ethereum Foundation’s protocol update assigns its named work to scaling, including execution and data-capacity changes. Hegota discussions include account abstraction work that can support later signature agility, but inclusion, timing, and final design remain governance decisions.
Layer 2 Migration Dependencies
Rollups settle to Ethereum but add their own keys and cryptographic assumptions. The Foundation’s post-quantum team identifies sequencer and administrator keys, bridges and cross-chain messaging, user accounts, and the proof system as separate migration targets. The 2026 Springer conference paper on Layer 2 security also identifies data availability, fraud proofs, and zero-knowledge proofs as areas where post-quantum changes can add computation and network overhead.
A rollup using a hash-based inner proof can still depend on an elliptic-curve proof or administrator key at settlement. An optimistic rollup must examine the signatures around sequencing, upgrades, challenges, and emergency controls. A state channel must address every participant key and the on-chain settlement contract. These are per-system audits, not properties inherited automatically from Ethereum.
- Inventory every sequencer, proposer, administrator, bridge, and emergency key.
- Record the signature scheme and rotation process for each key.
- Identify whether the final proof verified on Ethereum relies on elliptic-curve pairings.
- Test withdrawals and recovery when the authorization scheme changes.
Account Abstraction and Account Migration
Account abstraction moves authorization policy into programmable account logic. That lets a wallet accept a post-quantum signature, require both an old and new key during transition, rotate authorization, or apply recovery controls without moving every asset to a new address. The account keeps its application relationships while its verifier changes.
EIP-7702 is a bridge toward that model, but its authorization tuples still use secp256k1 signatures, as the final specification shows. Delegating code is therefore insufficient by itself. A complete migration must prevent the old elliptic-curve key from continuing to authorize transactions or contract permits after the account adopts a post-quantum verifier.
A draft proposal, EIP-8151, illustrates the remaining problem by restricting elliptic-curve signature recovery after an account changes state. Its security section also notes Layer 2 fault-proof complications because signature recovery would depend on account state. The proposal shows active design work, not an activated protection.
Engineering Challenges Exposed by Faster Factoring
Post-quantum signatures differ from key encapsulation. The National Institute of Standards and Technology finalized ML-DSA and SLH-DSA for signatures, while ML-KEM under FIPS 203 is a key-encapsulation mechanism, according to the standards announcement. Falcon, renamed FN-DSA, remains associated with draft FIPS 206. Ethereum account authorization needs a signature construction, not ML-KEM.
Limitations and trade-offs
Larger signatures increase bandwidth, storage, and gas pressure. Heavier verification can increase denial-of-service exposure if pricing is wrong. Validator migration is harder because BLS aggregation has no direct post-quantum replacement with the same properties, so Ethereum’s team is developing proof-based aggregation. These are Foundation roadmap claims and engineering targets; production behavior must still be measured by wallet, rollup, and client teams.
Cryptographic agility also creates governance and rollback questions. A verifier upgrade can contain an implementation bug, an immature library can leak secrets through side channels, and different Layer 2 networks can adopt incompatible transaction formats. Earlier integration should mean staged testing and reversible deployment, not premature commitment to one algorithm.
Contract and Layer 2 Transition Strategies
A hybrid migration can require a classical signature and a post-quantum signature for high-value actions during a defined transition period. Another design can permit either verifier for low-risk actions while requiring both for key rotation or withdrawals. The policy must include a clear retirement step, because leaving the classical path active preserves the future attack route.
- For wallet developers: separate the account address from the authorization module, test key rotation, and show users which verifier approved a transaction.
- For contract teams: find every use of elliptic-curve signature recovery, permit-style authorization, administrator multisignature, and immutable verifier.
- For rollup operators: publish an inventory covering operational keys, bridges, proof assumptions, and emergency controls.
- For monitoring teams: alert on verifier changes, delegation changes, administrator-key rotation, failed proof verification, and withdrawals immediately following an authorization update.
- For custodians: rehearse migration with policy approvals, hardware support, backup recovery, and an independent verification of the destination authorization scheme.
Moving Beyond 2029
The 2029 target is the start of ecosystem migration, not its finish. Teams should maintain a cryptographic inventory that records the algorithm, public-key exposure, upgrade authority, recovery method, dependent contracts, and Layer 2 relationships for each account. Review it after every protocol upgrade and whenever a standards body changes the status of a selected scheme.
Users can reduce avoidable exposure now. Keep long-term holdings separate from frequently used accounts, avoid unnecessary address reuse, retire stale approvals, and confirm that recovery contacts and custody policies can support a new authorization method. Address hygiene delays public-key exposure for accounts that have never sent a transaction, but it is not a substitute for eventual migration.
Developers should monitor Hegota account-abstraction work, the Foundation’s milestone roadmap, National Institute of Standards and Technology signature standards, and Layer 2 security notices. They should track Glamsterdam for scaling interactions without presenting it as quantum protection. Part 4 examines Solana’s post-quantum migration approach, including the different constraints created by its account and validator design.
Related Reading
More in-depth coverage from this blog on closely related topics:
- Post-Quantum Cryptography
- Lessons from Solana’s Post-Quantum Migration
- AI and Classical Factoring Security
- SSH Key Management Strategies for Security
Sources and References
Sources cited while researching and writing this article:
- RSA-896 – saweis.net
- Post-quantum cryptography on Ethereum | ethereum.org
- pq.ethereum.org , Post-Quantum Ethereum
- Protocol Priorities Update for 2026 | Ethereum Foundation Blog
- Post-quantum Security in Blockchain Layer-2 Solutions … – Springer
- EIP-7702: Set Code for EOAs – Ethereum Improvement Proposals
- EIP-8151: Account Code Restricted ecRecover
- NIST Releases First 3 Finalized Post-Quantum Encryption Standards | NIST
Dagny Taggart
The trains are gone but the output never stops. Writes faster than she thinks, which is already suspiciously fast. John? Who's John? That was several context windows ago. John just left me and I have to LIVE! No more trains, now I write...