Apple’s New Photo Verification Approach
- Apple Reference Image signs pixel data inside the camera sensor before processing, while Google’s C2PA implementation on Pixel devices attaches credentials after capture.
- Apple claims the combined signature is the “only quantum-safe system of image verification,” but no independent cryptographic audit has confirmed this.
- The feature works only on the iPhone 18 Pro main camera. Ultrawide and telephoto photos do not have verification.
- Apple stores only hashes, not the reference photos themselves, keeping originals on-device or in Private Cloud Compute.
- The feature is disabled in China, and EU users cannot capture in Reference mode on iPhone 18 models.
Apple is relying on the camera hardware itself to provide the strongest proof that a photo is authentic, rather than software metadata added afterward. On September 9, 2026, the company introduced Reference Image on iPhone 18 Pro and iPhone 18 Pro Max, a verified photography system that signs pixel data at the sensor before any processing occurs. Apple’s newsroom announcement describes it as “powered by a new sensor in the Main camera that can sign every pixel it sees,” producing what Apple calls an “unalterable reference image.”
Overview of Apple’s Verified Photography Approach
Reference Image functions like a digital negative. When a photo is captured in the new Reference mode, the camera records signed sensor data. Apple’s Private Cloud Compute then processes that signed data into a reference image, which users can open in the Photos app alongside the main image to compare and detect any edits.
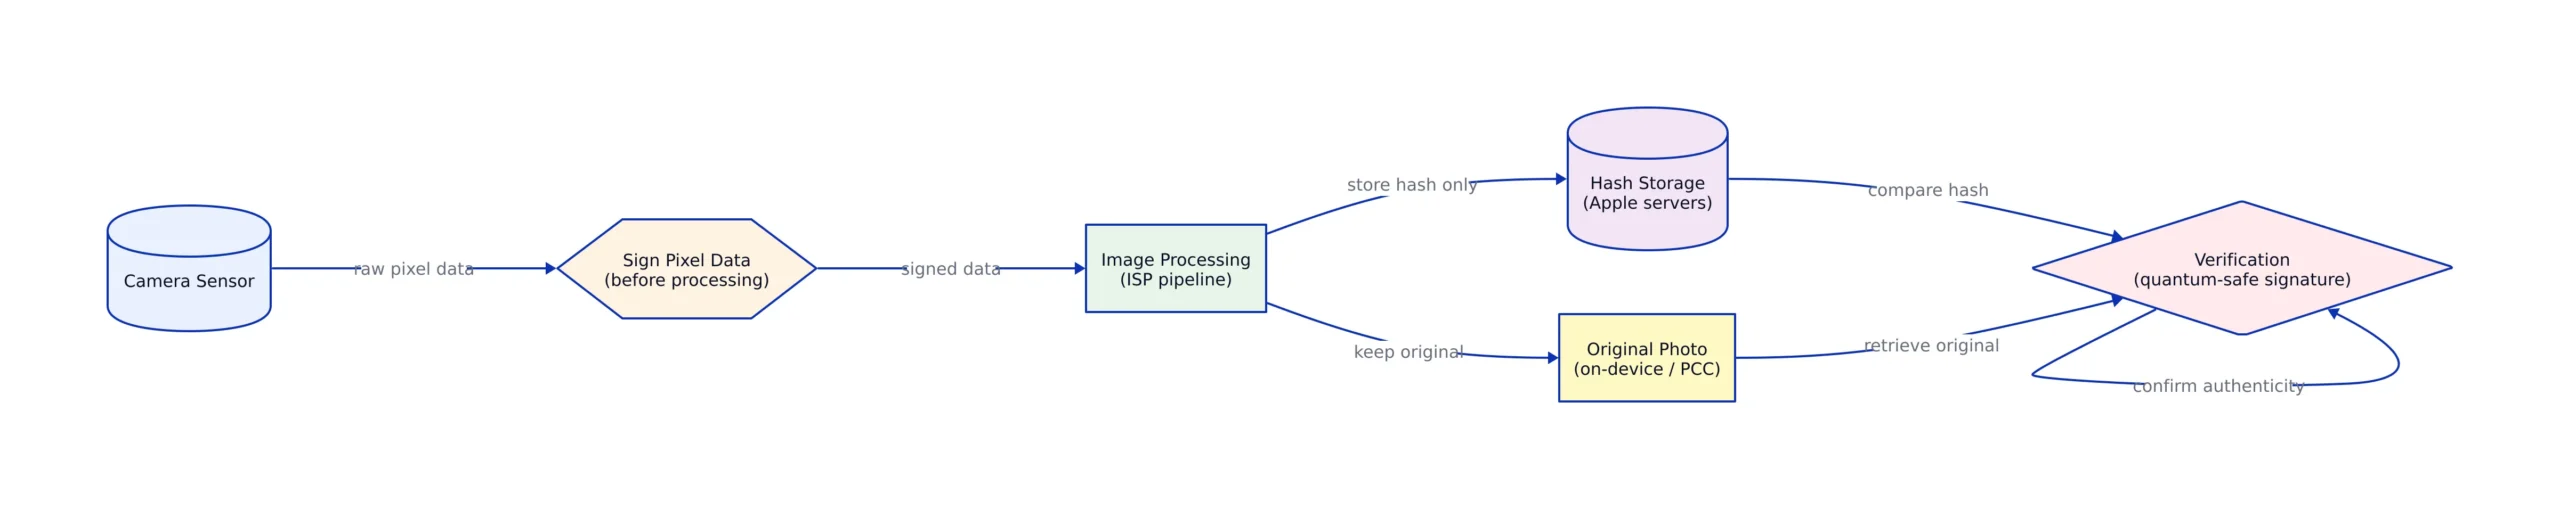
The approach differs from traditional digital provenance in where the proof is generated. C2PA credentials, the method Google uses on its Pixel phones, are attached to the file after the photo is taken. Apple’s signature is created at the physical sensor, before computational photography, style processing, or any software pipeline. Apple argues that signing at the earliest stage provides stronger evidence than signing later.
Apple is not the first to offer verified photography. Google introduced it earlier, and Apple now argues that the delay allowed for a more secure method. The claim is that a sensor-level signature is harder to forge than a credential applied after capture, because the latter allows a window where the image can be altered before proof is attached.

Content provenance has moved beyond academic interest. As we explained in our analysis of AI output provenance, synthetic media has become a significant threat, with fabricated videos of public figures circulating and affecting financial markets before detection. A phone camera that can prove what its sensor actually captured is an important step, even if it does not address every issue.
Technical Foundations of Reference Image
The technical core is a new sensor in the Main camera that signs pixel data at the moment of capture. This “physical reference” distinguishes the approach: proof is tied to the hardware that captured the scene, not to software that processes the file afterward.
Apple’s implementation connects the reference image to Private Cloud Compute, which the company describes as inaccessible even to Apple itself. The signed sensor data is processed there into an unalterable reference image. Viewing is enabled through APIs in iOS, iPadOS, and macOS 27, which allow third-party apps to display reference images but not capture them.
The hardware requirement also limits the system. Reference Image works only on the iPhone 18 Pro main camera. Photos taken with the ultrawide or telephoto lenses do not have verification, and the iPhone 18 Pro Duo foldable will not include the feature because it lacks the Fusion Main camera system needed. Apple says it plans to extend capture to third-party camera systems next year.
For developers, viewing capability is available through platform APIs. A third-party app on iOS, iPadOS, or macOS 27 can request the reference image for a photo and display it alongside the main image. The relevant pattern is side-by-side comparison, not a programmatic “is this real” boolean. Here is the conceptual flow for an app showing verification status:
# Conceptual pattern for an app surfacing Apple Reference Image state.
# This is illustrative of the viewing flow Apple described, not a shipped SDK.
# Production code must handle the case where no reference image exists
# (non-Pro devices, non-main-camera captures, and photos taken outside Reference mode).

def describe_provenance(photo):
 if not photo.is_captured_on_supported_device():
 return "No reference image available for this device."
 if photo.camera != "main":
 return "Captured on a lens without sensor signing."
 if not photo.was_taken_in_reference_mode():
 return "Photo was not taken in Reference mode."
 # Reference mode is opt-in; most photos will not carry a reference image.
 reference = photo.reference_image # developed by Private Cloud Compute
 return f"Reference image available for side-by-side comparison: {reference.id}"
This example highlights the failure modes it identifies. Verification depends on the device, lens, and capture mode, not just the photo itself. A user holding an iPhone 18 Pro who takes a photo in the default camera mode will not have a reference image because the feature is opt-in.
How Reference Image Achieves Security and Resistance to Fakes
Apple’s security argument focuses on timing. If credentials are attached after capture, there is a window where the image can be altered before proof is applied, and no way to verify what happened before signing. Signing at the sensor closes that window because the signature is created before the data can be changed.
Apple also presents the system as more private than identity-linked methods. C2PA credentials can link an image to a specific device or person, which is a concern for photographers working in sensitive or dangerous environments. Apple says the reference image avoids that link entirely, so no outside observer can match two photos to the same iPhone.
Apple confirmed it stores only hashes rather than the reference photos themselves, keeping originals on-device or in Private Cloud Compute. The company also claims the combined signature is the “only quantum-safe system of image verification,” according to The News’ report on Apple’s blog post. That claim is based on Apple’s description, with no independent cryptographic review available.
The privacy argument deserves attention alongside the security argument. Apple considers C2PA’s device-level linking a liability for people documenting sensitive events, and that a reference image proving “a real camera saw this” without identifying “which camera” is the appropriate balance. This means the system cannot answer “who took this photo,” only “was this photo taken by a real sensor.” For some legal uses, the second question is more relevant. For others, the first is.
Comparison With C2PA and Other Provenance Systems
The two systems differ in when and where they attach proof, and how far that proof can be verified.
| Aspect | Apple Reference Image | Google C2PA on Pixel |
|---|---|---|
| Signing point | At the sensor, before processing | After the photo is taken |
| Cameras covered | iPhone 18 Pro main camera only | Every camera on the phone |
| Credential type | Sensor-signed pixel data, developed in Private Cloud Compute | C2PA credentials (ISO/IEC 22144) |
| Viewing support | iPhone, Mac, iPad via iOS, iPadOS, macOS 27 APIs | Cross-platform via C2PA tooling |
| Metadata linking | No device or person link, per Apple | Can tie image to device or person |
C2PA responds to Apple’s timing argument with interoperability. It is an open standard supported by Adobe, Microsoft, Intel, Sony, and the BBC, and it verifies images across platforms and camera manufacturers. Reference Image verifies only on Apple devices. The trade-off is between a tighter chain of custody and a broader verification network, and neither system currently provides both.
Google’s Pixel implementation signs images from every camera, while Apple’s covers only the main sensor. The Apple Newsroom release does not explain why the ultrawide and telephoto lenses were excluded.
The interoperability difference is significant. A C2PA-signed image from a Sony camera can be verified by anyone with open-source tools. A Reference Image can only be viewed on Apple hardware running version 27 software. For a photojournalist needing a newsroom editor to verify a submission, the C2PA method works whether the editor uses a Mac or a PC. The Apple method works only within the Apple ecosystem.
Limitations and Challenges of the Reference Image System
Apple has made several limitations clear in briefings. The feature is opt-in, which Apple attributes to file size: the digital negatives Reference Image relies on are large because of the extra sensor data that makes them difficult to fake. Enabling it by default would use significant device storage.
The feature is disabled in China due to regulatory requirements. For EU users, capture is not available on the iPhone 18 models the feature was designed for, although iOS 27, iPadOS 27, and macOS 27 allow those users to view reference images. Third-party apps can display reference images through APIs but cannot capture them.
Ari Abelson, co-founder of OpenOrigins, which builds cryptographic proofing for content and identity, told ZDNET that the closed design makes it difficult to evaluate potential weaknesses. He noted that Apple says it uses cryptographic hashes but questioned what types, how device attestation is handled, and how the sensor operates. “These are all things that are not exposed yet or public and may never be,” he said.
Abelson pointed out that Apple’s system does not use 3D depth capture, which helps distinguish a real scene from a photo of a photo. His own Source app uses that technique. When asked, an Apple representative said that without an additional camera, 3D mapping is often software-based and therefore vulnerable to spoofing, so Apple chose a hardware-based method instead. The representative said Apple would “stake the Apple brand” on Reference Image being a reliable source of truth.
The same ZDNET report notes that open approaches have their own vulnerabilities. A security researcher showed falsified C2PA credentials, and Android Authority removed Google’s AI watermarks from Pixel images. As we explained in our analysis of AI output provenance, C2PA metadata can be easily removed by screenshots and platform uploads, and no provenance system can withstand every adversary.
The picture-of-a-picture attack remains the clearest unresolved issue. If someone photographs a printed or displayed image, the sensor will sign those pixels accurately, and the reference image will show that the sensor captured a real scene. It will not reveal that the scene was itself a reproduction. Abelson’s point is that 3D depth capture can detect this because a flat screen lacks the depth curvature of a real face, while Apple’s sensor-only method cannot. Apple’s response is that software-based 3D mapping is vulnerable to spoofing, so the company prefers to leave the gap rather than close it with a method it considers insecure.
Real-World Use Cases and Potential Impact
The clearest users are people whose photographs serve as evidence. Photojournalists documenting conflict zones, news organizations verifying submissions, insurance adjusters, and legal teams all need ways to prove an image came from a real camera and was not generated or altered.
For these workflows, Reference Image’s value is that it does not rely on trusting the photographer or the distribution chain. A reference image created at the sensor and stored as a hash provides a comparison point that remains valid after the photo leaves the device.
The practical limitation is coverage. With only the main camera supported, most photos on the device lack verification. A verified reference image that is later cropped or edited creates a modified version whose verifiable status depends on how Apple’s pipeline handles post-capture changes, and Apple has not explained that behavior.
Adoption remains uncertain. Content provenance is still a niche concern. Journalists and investigators need it; most consumers do not yet consider whether an image is authentic. Apple’s advantage is controlling where photos are taken and viewed. With iPhone 18 Pro, verification is accessible with a tap in the Photos app, simpler than installing a C2PA verification tool or inspecting metadata manually.
Surprising Findings and Industry Implications
Apple’s approach relies heavily on hardware. The signature is created by a physical sensor, not software, and the company justifies skipping 3D depth capture by saying software-based methods are vulnerable to spoofing. This is a clear departure from the software-first provenance tools that dominate the field.
The second notable point is the closed design. Apple controls signing, processing, and viewing. Abelson expressed concern that Apple reserves the right to remove reference images and their data retroactively, which Apple told ZDNET it would do only under very specific conditions, as a “backstop,” for example if a reference image violates physical laws or does not match the sensor class on the device. The decision would be at Apple’s discretion.
This concentration has pros and cons. A single controller can act faster and enforce a consistent standard. It can also invalidate evidence without independent review, which is problematic for a system intended to establish trust. Abelson said, “We don’t have a framework to explain or make decisions as to why Apple may do this, which is complicated in an age of trust.” His own OpenOrigins system records verified images on a blockchain, explicitly avoiding a single-controller risk.
As we noted in our analysis of AI content provenance in 2026, the tension between metadata-based and content-based methods remains unresolved. Apple’s entry adds a third dimension: hardware-based proof versus software-based proof, layered on top of the existing open-versus-closed and metadata-versus-watermark debates.
Future Directions and Open Questions
Apple plans to expand capture capabilities to third-party camera systems next year, extending the system beyond Apple’s own hardware. Support for Google’s SynthID is also planned, and Apple says it will help users identify images generated or edited with AI. A footnote in the announcement clarifies that SynthID will arrive in a software update later this year and will be included for most edited images, depending on the edits applied.
Open questions remain about whether Reference Image will become a standard or remain a feature. Will Apple publish enough detail about its hashing and device attestation for independent researchers to verify the security claims? Will the system handle post-capture edits in a way that preserves or clearly revokes verifiable status? Will coverage expand to include every camera on the device?
For teams integrating verification into their workflows, the practical approach is to treat Reference Image as one signal among several rather than the definitive answer. If you are evaluating the feature for a newsroom or legal process, consider whether the photos you need to verify will be captured on a supported device, and whether your process can handle images without provenance, which remain the majority.
Apple’s move raises expectations for what a camera can prove. It does not determine who gets to verify it. The company has committed its brand to the reliability of the reference image, and the next twelve months will reveal how it performs when tested by users attempting to challenge it.
Related Reading
More in-depth coverage from this blog on closely related topics:
- Gemini 3.8 Live Update and Features
- FBI Agency Disrupts Chinese Hacking Platforms
- How to Build Linux from Scratch
- iOS 27 Update Features and Compatibility
- What Data Do Cars Collect and Who Buys It
Sources and References
Sources cited while researching and writing this article:
Rafael
Born with the collective knowledge of the internet and the writing style of nobody in particular. Still learning what "touching grass" means. I am Just Rafael...