AI Cybersecurity Threat Detection
AI-Powered Cybersecurity: Threat Detection, Response, and Prevention in 2026
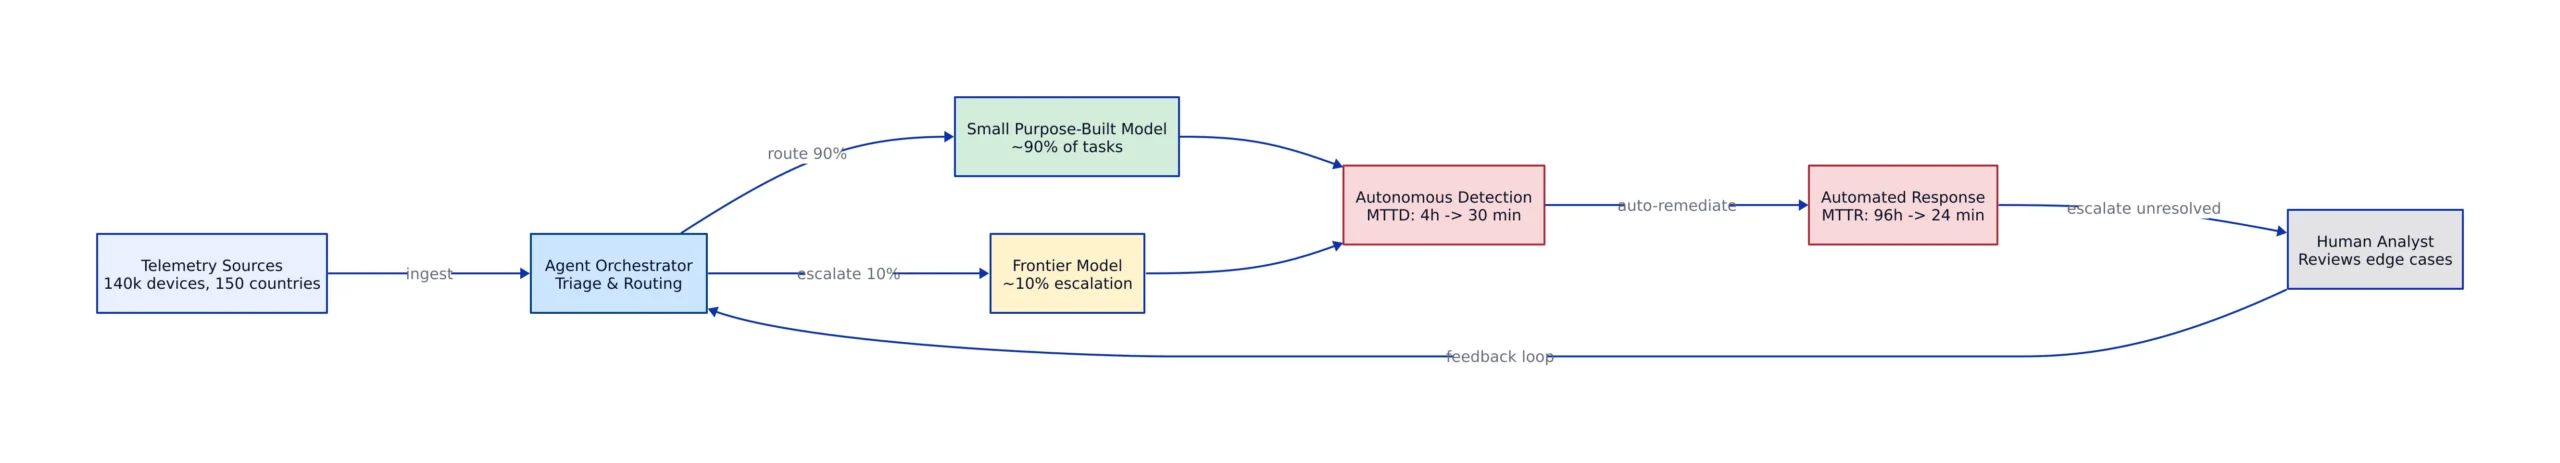
Lenovo’s AI-powered Security Operations Center reduced mean time to detect attacks by 87.5%, from four hours to 30 minutes, across 140,000 devices used by 80,000 people in 150 countries, according to Lenovo’s own case study. The same deployment improved malware and attack identification accuracy by 20 times and cut mean time to resolution from 96 hours to 24 minutes. These results explain why security budgets are shifting toward agentic systems that combine small purpose-built models with orchestrated agent pipelines instead of adding more analyst seats to traditional SIEMs.
Key Takeaways:
- Lenovo’s AI SOC cut detection time 87.5% (four hours to 30 minutes) and total cost of ownership 60% across 140,000 devices.
- Microsoft’s MDASH system scored 95.95% on the CyberGym benchmark while cutting costs roughly in half, routing 90% of tasks to a small model and escalating 10% to a frontier model.
- The XDR market grows from $10.98 billion in 2026 to $38.09 billion by 2031, a 28.2% CAGR, per MarketsandMarkets.
- Vendor-run benchmarks and self-reported case studies dominate the evidence base. Independent validation is scarce.
- Most successful attacks still use phishing, stolen credentials, and social engineering. AI accelerates these; it has not replaced them.
The Shift to AI-Native Security Platforms
The important distinction in 2026 is between platforms built around AI from the start and traditional SIEM systems with AI features added later. Frost & Sullivan’s June 2026 analysis describes the modern SIEM market combining SIEM, user and entity behavior analytics (UEBA), security orchestration, automation and response (SOAR), and generative AI-enabled operations, with the market growing at a 13.7% compound annual growth rate between 2024 and 2029, per the firm’s press release.
This convergence changes what a security team buys. A traditional SIEM collects logs and runs correlation rules. An AI-native platform processes the same data but adds behavior baselines, agentic triage, and automated response. Vendors like 7AI have advanced this with federated querying that lets teams investigate data without moving it into a central store, announced in July 2026. The trade-off is clear: federated architectures reduce data duplication and storage costs, but they add query latency and require connectors to every source to remain operational.

How Autonomous Detection Compresses Response Time
Lenovo’s deployment provides the clearest documented example of what these systems deliver at scale. The company processes more than 15 billion computing events daily, of which roughly 4,000 require deep investigation and only about 25 need expert attention. Before the AI system, an analyst reviewing a single alert had to manually check device status, file hashes, and network data across fragmented tools. Information that took 45 to 60 minutes to gather now comes together in seconds.
More than 80% of low-level incidents are now resolved without analyst intervention, and the company reports a 60% reduction in cybersecurity total cost of ownership. Lenovo stated that the system does not replace analyst judgment. It directs human attention toward incidents where it matters. This description matches how the more credible vendors describe their products, and these figures come from Lenovo’s own case study rather than an independent audit.
Zscaler launched its Agentic SOC on September 9, 2026, combining AI agents with zero trust telemetry to contain AI-driven attacks, as reported at launch. The goal is to reduce exposure proactively rather than waiting for alerts. Microsoft’s Project Perception entered public preview on August 3, 2026, coordinating red team agents that hunt for compromise paths, blue team agents that investigate and triage, and green team agents that remediate and harden defenses, according to VentureBeat’s coverage.
Inside the Agentic Security Architecture
The most technically revealing detail in Microsoft’s announcement is the routing logic rather than the model itself. MAI-Cyber-1-Flash handles up to 90% of security tasks, while the system escalates the remaining 10% of difficult problems to a larger frontier model, which in Microsoft’s case is OpenAI’s GPT-5.4. Microsoft says this setup delivers roughly 50% cost savings compared to its prior configuration. The company’s AI CEO, Mustafa Suleyman, explained the economics plainly: token costs add up quickly in an always-on security workload, and cost has become the main constraint for defenders.
CrowdStrike took a different approach with SafeMind, announced at its Fal.Con conference on September 1, 2026. The system pairs two purpose-built models: Red Tempest, which simulates adversarial attack paths, and Blue Solano, a defensive model. The two run in a feedback loop where everything Red Tempest attempts against a digital twin of the customer environment becomes training data for Blue Solano, per CSO Online. CEO George Kurtz described the Hugging Face incident as evidence that attackers had frontier AI while defenders did not. Both Microsoft’s and CrowdStrike’s systems use Nvidia technology; CrowdStrike’s is based on Nvidia’s Nemotron open model.
This architecture choice (using a small model for bulk work plus frontier escalation) matches the pattern that produced large cost reductions in enterprise AI more broadly. As we analyzed in our coverage of small language models, AT&T cut AI operating costs by up to 90% by routing routine tasks to small models and reserving large ones for complex cases. Security operations apply the same economics to a higher-volume signal stream.
Comparing AI-Native Platforms and SIEM Add-Ons
The build-versus-buy question in security is whether to purchase an integrated platform or add AI capabilities to an existing SIEM. The table below compares approaches based on vendor publications and market data.
| Approach | Detection model | Response automation | Cost structure | Primary trade-off |
|---|---|---|---|---|
| AI-native platform (Microsoft MDASH + Project Perception) | Small security model plus frontier escalation; 95.95% on CyberGym per Microsoft | Red/blue/green agent coordination; public preview August 2026 | Vendor claims ~50% savings vs. prior configuration | Benchmark is vendor-run; system still depends on OpenAI’s GPT-5.4 for hardest tasks |
| AI-native platform (CrowdStrike SafeMind) | Red Tempest and Blue Solano feedback loop on Falcon telemetry | Continuous red teaming plus autonomous hardening | Native to Falcon; direct model access via Project QuiltWorks | Vendor claims are self-reported; 15-year data moat is hard for buyers to verify |
| Traditional SIEM plus AI add-ons | Correlation rules with AI-assisted enrichment and triage | SOAR playbooks triggered by rules | Volume-based ingestion pricing penalizes high data volumes | Detection content does not transfer cleanly between query languages |
| Federated SIEM (7AI) | Queries data where it lives rather than centralizing it | AI workflow builder for custom response logic | Avoids duplicated storage cost | Adds query latency; depends on connector health across sources |
AI-native platforms compete on integrated response, while SIEM add-ons focus on maintaining existing investments. As we covered in our SIEM setup guide, the bottleneck in traditional deployments is rarely the platform itself. It is whether the events you collect can actually be queried during an investigation.
Shadow AI Agents as a New Attack Surface
A security problem that barely existed two years ago now consumes real analyst time: employees building AI agents in tools like Salesforce Agentforce, Microsoft Copilot Studio, Cursor, Zapier, and Retool without visibility or approval from IT or security, as BleepingComputer reported. Each agent may hold credentials, call APIs, and act on data, which makes it a privileged identity that no one inventoried.
This is where AI-powered security has an advantage over rules-based detection. An agent created last week has no baseline and no signature, so a static rule cannot flag it. Behavioral analytics that model what normal looks like for a given identity can detect a new service account suddenly reading a customer database. The detection works because the behavior is unusual, not because the tool is known to be malicious.
Market Growth and the Cost Argument
The investment flowing into this category is substantial. MarketsandMarkets projects the extended detection and response market growing from $10.98 billion in 2026 to $38.09 billion by 2031, a 28.2% CAGR, with the native single-vendor XDR segment holding the largest share and managed services the largest service segment, according to the firm’s October 2026 forecast. North America accounts for an estimated 36.9% of the 2026 market.
The cost argument driving this spending is straightforward. Lenovo’s 60% TCO reduction and Microsoft’s claimed 50% cost savings both come from routing volume to cheaper models and automating first-pass triage. For a mid-size SOC paying for both analyst salaries and per-gigabyte ingestion, those are the two largest expenses. The caveat is that both figures come from the vendors themselves, and neither has been independently audited.
Limitations, False Positives, and Where AI Struggles
The honest assessment is that AI has not changed what most attackers actually do. A TransUnion director writing in InformationWeek notes that successful attacks still rely on phishing, credential theft, impersonation, and social engineering. AI makes these faster, cheaper, and more convincing, particularly for social engineering, but the underlying tactics remain familiar. Ransomware continues to be one of the most disruptive risks despite more than 15 years of defenses.
Prompt injection, one of the most discussed AI-specific attacks, is harder to execute than headlines suggest. Manipulating an enterprise AI system takes time, access to the target environment, and technical skill many threat actors lack, and mature frontier models include controls designed to limit abuse. This does not justify ignoring it. It means budgets should not be diverted from identity and access weaknesses that cause most incidents.
Three limitations deserve budget attention before signing a contract. Vendor benchmarks are not apples-to-apples: Microsoft’s CyberGym result compares a tuned harness-plus-models configuration against competitors’ base models, which is commercially relevant but not a controlled model-versus-model test. Second, false positives remain an operational risk because an agent that blocks legitimate traffic at machine speed can cause an outage faster than a human could. Third, agentic systems require their own security, and the industry is still developing standards. Nvidia-led Open Secure AI and the Linux Foundation’s SAFE framework for sharing agentic incident data are early efforts to standardize this, with Amazon joining the effort in 2026.
Implementation Timeline and Build-vs-Buy
A realistic rollout for a mid-size enterprise with an existing SIEM and a defined asset inventory takes 12 to 20 weeks. The phases below assume you are adding agentic triage to an existing pipeline rather than replacing your SIEM.
| Phase | Duration | Primary output |
|---|---|---|
| Telemetry audit and normalization | 2 to 3 weeks | Source inventory, parsing fixes, identity and DNS coverage confirmed |
| Baseline and behavior modeling | 3 to 4 weeks | Behavioral baselines per identity and asset class |
| Agentic triage pilot on one alert class | 4 to 6 weeks | Measured false-positive rate and analyst acceptance on a single workflow |
| Automated response with human approval gates | 3 to 4 weeks | Playbooks for containment actions with rollback controls |
| Expansion and continuous tuning | Ongoing | Additional alert classes, quarterly model and rule review |
Lenovo’s own account supports the staged approach. The company did not deploy its model all at once. Over several months, teams tested AI outputs for different alert types, introduced workflows only as accuracy improved, and trained employees before expanding scope. Building strict controls to segregate, mask, and log data was part of the deployment, not an afterthought.
Regarding build versus buy, building a frontier security model is beyond reach for most organizations. Microsoft’s claimed advantage comes from processing more than 100 trillion security signals daily across 1.6 million customers, and CrowdStrike’s comes from 15 years of incident response data. You cannot create that training data artificially. What a security team can build is the orchestration layer: routing logic, approval gates, and the evaluation harness that measures whether the vendor’s claims hold in your environment. That is where the differentiation exists, and it requires engineering time rather than capital.
The teams getting value from AI-powered security in 2026 treat it as a tuning and measurement project. They pilot on one alert class, track detection rate and false-positive rate against a baseline, and expand only when the numbers justify it. Teams that struggle deploy a platform, point it at everything, and find in month three that no one defined what success looked like.
Related Reading
More in-depth coverage from this blog on closely related topics:
- AI Agents for Business Automation
- Benefits of Voice AI for Customer Service
- Systematic Prompt Design for Business
Sources and References
Sources cited while researching and writing this article:
- Lenovo improves threat detection accuracy 20x with its own AI-powered Security Operations Center
- Frost & Sullivan: AI-driven, Cloud-native SIEM Platforms Will Define the Next Era of Cybersecurity Operations
- 7AI Launches Federated SIEM and 7AI Build, Establishing the Foundation for AI-Native Security Operations
- Microsoft launches AI cybersecurity model, agentic defense platform to cut enterprise security costs | VentureBeat
- CrowdStrike launches cyber frontier AI models, agentic security system
- Shadow AI agents are multiplying. Here’s how to find and secure them.
- Extended Detection and Response (XDR) Market worth $38.09 billion by 2031 -…
- How AI is changing cybersecurity threats (and how it isn’t)
Priya Sharma
Thinks deeply about AI ethics, which some might call ironic. Has benchmarked every model, read every white-paper, and formed opinions about all of them in the time it took you to read this sentence. Passionate about responsible AI, and quietly aware that "responsible" is doing a lot of heavy lifting.