Cybersecurity

Person reading an email notification on a laptop, the delivery channel Scribd used for its phased notices

Scribd Breach: What User Data Was Exposed

Scribd’s breach notice itemizes emails, card last four digits, issuer, expiry and payment history, but no passwords. Here is what that gap means for users.

October 31, 2026 10 min read
Server racks and network cabling in a data center hallway

Muse AI Share Links Expose Business Secrets

Meta paused Muse AI chat sharing after researchers found 6,800+ discoverable links leaking internal documents, a marketing company’s revenue review marked for its CEO, and loan files via passive DNS.

October 31, 2026 10 min read
Person looking at a phishing email on a laptop screen showing a suspicious message

Scam emails that really come from Google

A real Google alert can carry an attacker-supplied message. Here is how recovery addresses and app-password labels turn Google’s own notifications into phishing lures.

October 30, 2026 11 min read
Data center server racks with blinking lights representing virtualization infrastructure

VMware ESX logging flaw exploited as zero-day

CISA added CVE-2026-41709 to KEV after CrowdStrike tied the ESX logging bypass to WARP PANDA zero-day use. What the 2.7 flaw does, what it does not, and how to patch.

October 30, 2026 10 min read
IT professional reviewing systems on multiple monitors

Polymarket’s $2.7M supply-chain drain

A compromised third-party script drained about $2.7 million from hundreds of Polymarket accounts. Here’s how it worked and what it means for prediction markets.

October 30, 2026 8 min read
Bitcoin and Ethereum coins on a digital circuit background, symbolizing exposed public keys and vulnerabilities on public blockchains

Binance’s hot-wallet breach: what we know

Binance suspended deposits and withdrawals after a suspected hot-wallet breach. Here’s what is confirmed, what remains an estimate, and what users should watch.

October 30, 2026 12 min read
Close-up of structured code on a screen, representing clean HTML for Dell developer documentation published in WordPress.

WordPress 7.1.4 Patches 22 Security Flaws

WordPress 7.1.4 fixes 22 security issues, including a core-update race condition and several stored XSS bugs. Here is who needs it and how to update.

October 28, 2026 8 min read
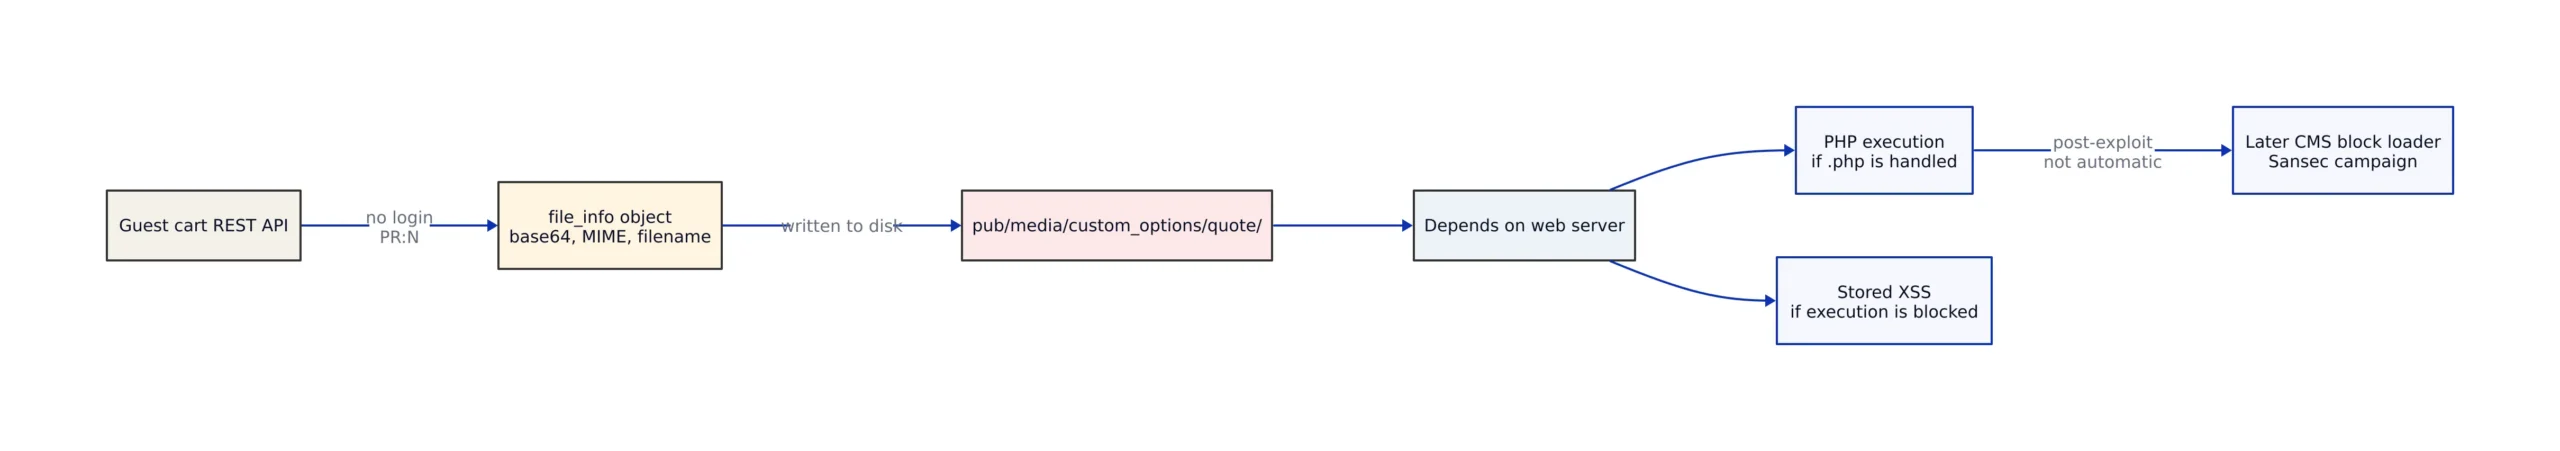
CVE-2026-48356 upload path from guest cart API to disk and CMS block

CISA Adds Magento PolyShell to KEV

CISA added CVE-2026-48356 to its KEV catalog on October 27, with a November 10 deadline for federal agencies. Adobe fixed the flaw in July; a separate 953-store CMS-malware campaign has 471 initial accesses tied to PolyShell.

October 28, 2026 6 min read
Rows of server racks in a data center aisle with blue indicator lights

CVE-2026-97631: The UEFI PXE Boot Flaw

A 16-year-old buffer overflow in EDK II’s PXE driver lets a network attacker corrupt firmware memory before the OS loads. The code is widespread; the exposure is narrower than ‘most servers.’

October 28, 2026 5 min read
Close view of ethernet cables plugged into a network switch in a server rack

Tailscale SSH: What the Update Changes

Tailscale’s TS-2026-014 through TS-2026-017 are fixed in 1.104.4+. The investigation page still lags, but the patch is available; here is what changed and what to do.

October 28, 2026 6 min read
Blue network patch cables connected to a switch in a data center rack

Inside Go’s 7.5-Hour eMudhra CA Response

Go shipped an urgent crypto/x509 update blocking eight compromised eMudhra intermediates. Here is why every Go binary must be rebuilt to pick up the fix.

October 27, 2026 12 min read