Blog

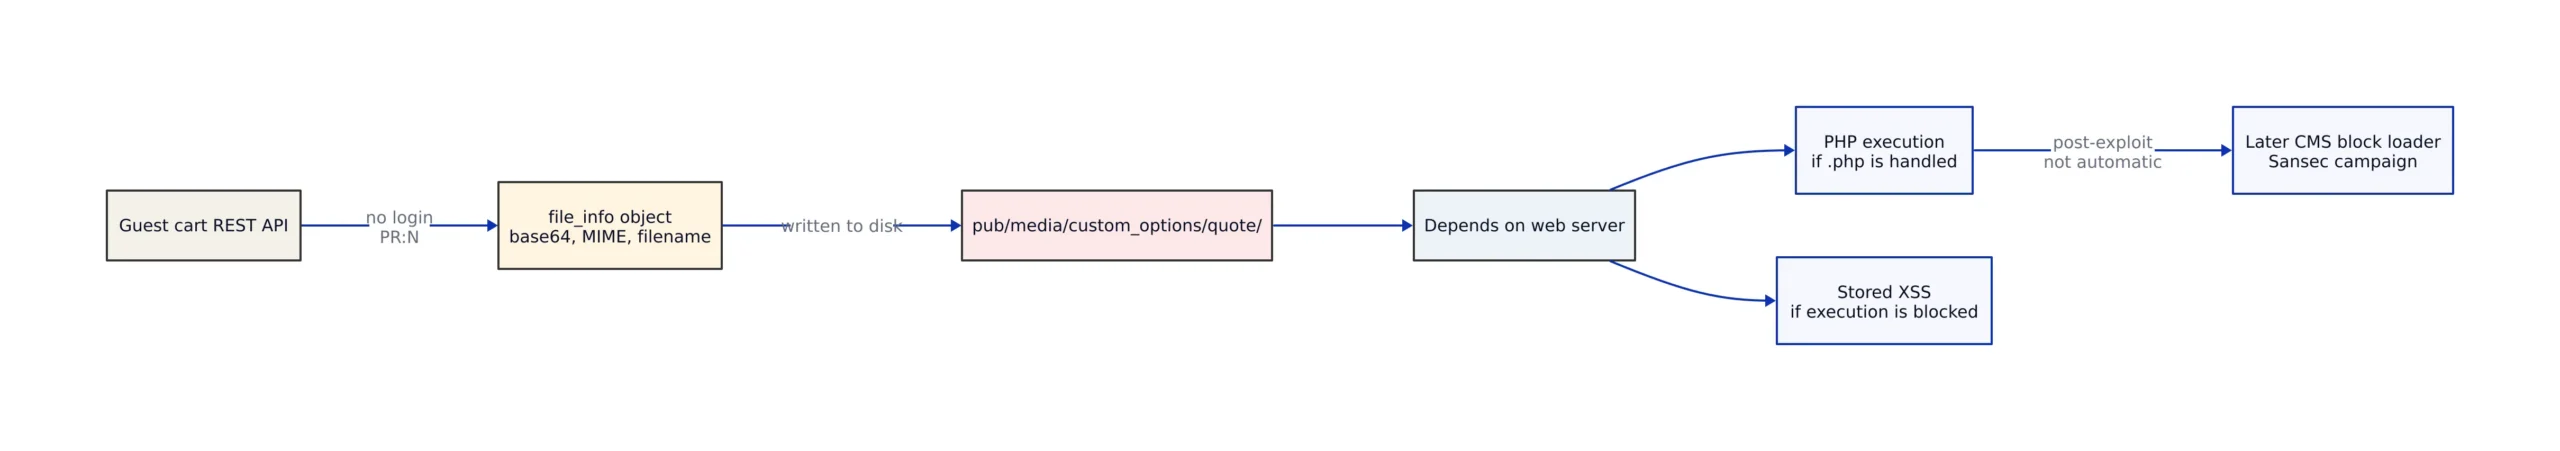
CVE-2026-48356 upload path from guest cart API to disk and CMS block

CISA Adds Magento PolyShell to KEV

CISA added CVE-2026-48356 to its KEV catalog on October 27, with a November 10 deadline for federal agencies. Adobe fixed the flaw in July; a separate 953-store CMS-malware campaign has 471 initial accesses tied to PolyShell.

October 28, 2026 6 min read
Rows of server racks in a data center aisle with blue indicator lights

CVE-2026-97631: The UEFI PXE Boot Flaw

A 16-year-old buffer overflow in EDK II’s PXE driver lets a network attacker corrupt firmware memory before the OS loads. The code is widespread; the exposure is narrower than ‘most servers.’

October 28, 2026 5 min read